Turn it on per domain
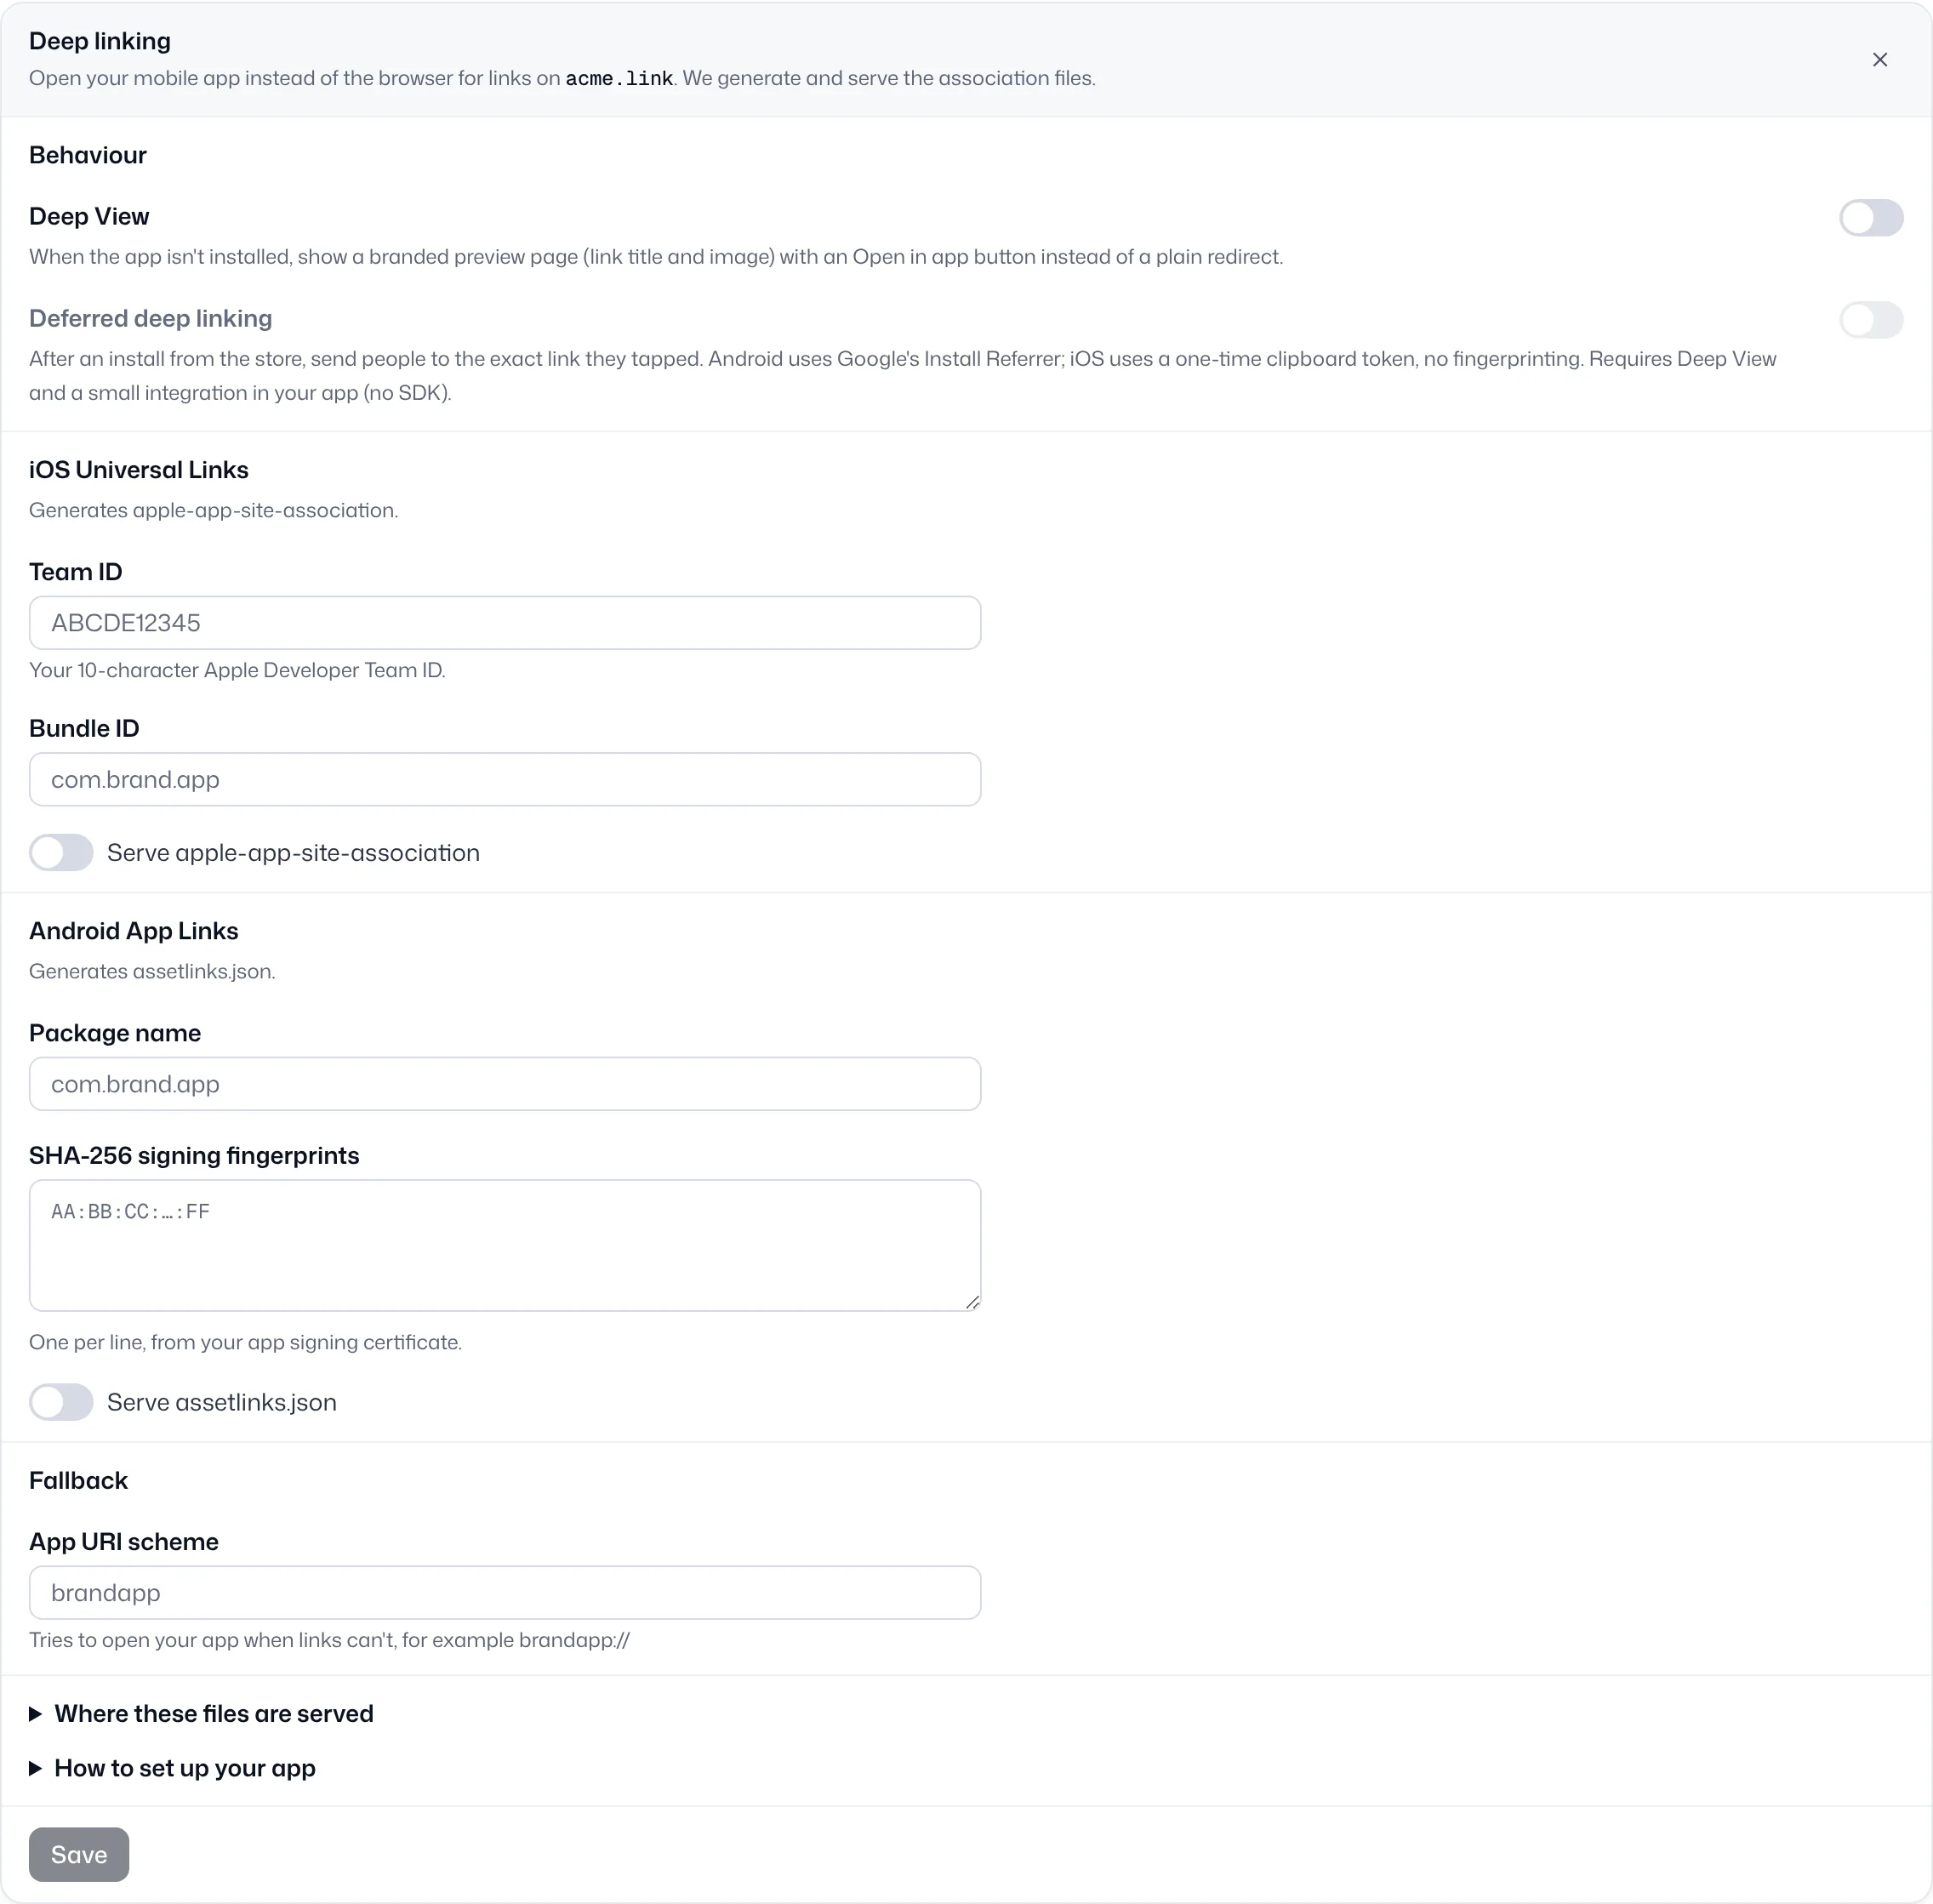
Switch on Deep View and deferred deep linking in each domain’s deep linking settings. Deep View shows a branded preview with an Open in app button.
Deferred deep linking
Deferred deep linking keeps a link’s destination through an app install: someone without your app taps the link, installs from the store, and opens on the exact screen the link pointed to. SwiftURL does it with the Play Install Referrer on Android and a one-time clipboard token on iOS, with no fingerprinting and no SDK.
Standard deep linking opens your app when it is already installed. Deferred deep linking covers the harder case: the app is not installed yet. SwiftURL mints a one-time token at the moment of tap, hands it to the store install, and your app redeems it on first launch to recover the exact destination and in-app path. The token is opaque, single-use, and short-lived, so an edit or delete between tap and install can never move where the user lands.
Switch on Deep View and deferred deep linking in each domain’s deep linking settings. Deep View shows a branded preview with an Open in app button.
Android reads the Play Install Referrer; iOS reads a user-initiated clipboard token. The same domain settings serve your Universal Links and App Links.
A one-time, opaque token carries the destination through the store install. Your app posts it to /track/open and gets back the destination and path. No IP matching and no device signals: the token itself is the only credential.
POST /api/v1/track/open
Content-Type: application/json

{ "token": "<opaque token>" }
200 OK
{
"destination": "https://acme.com/product/123",
"deepLinkPath": "product/123",
"linkId": "lnk_…"
} The Deep View preview offers to get the app, and mints a one-time token.
The token rides along via the Install Referrer on Android or the clipboard on iOS.
Your app posts the token to /track/open and gets back the destination and path.
The user opens exactly where the link pointed, first session included.
New installs land on the promoted content, not a generic home screen.
A deterministic token beats guessing which install came from which tap.
No IP correlation means one less privacy liability for your app.
No. Most incumbents recover the deferred link on iOS by matching people probabilistically on their IP address, which is personal data under DPDP and GDPR and exactly the fingerprinting we refuse to do. SwiftURL uses a user-initiated clipboard token on iOS and the official Play Install Referrer on Android instead. The token stores only a snapshot of the target, never a person, and it is purged after a short expiry.
Deferred deep linking keeps a link’s destination through an app install. Someone who taps a link without your app installs it from the store and, on first launch, still lands on the screen the link pointed to.
A one-time, opaque token is minted at the tap and recovered on first launch: on Android from the Play Install Referrer, and on iOS from a user-initiated clipboard token. Your app redeems it to get the destination and in-app path.
No. SwiftURL never matches people by IP address, screen size or other device signals. The token itself is the only credential, which keeps the approach aligned with GDPR and India’s DPDP Act.
No SDK. Your app needs a few lines of integration: on first launch it posts the token to the /api/v1/track/open endpoint and routes to the path that comes back.
The token is single-use and short-lived, expiring after one hour by default. It stores only a snapshot of the destination, never personal data, and is purged after it expires.
Deferred deep linking is included from the Pro plan, alongside standard deep linking. Turn it on per domain in the deep linking settings.
Open your app to the right screen when installed, with clean fallback to store or web.
Learn moreGeography, device, referrer and UTM, bot-filtered, with growth insights that surface what changed.
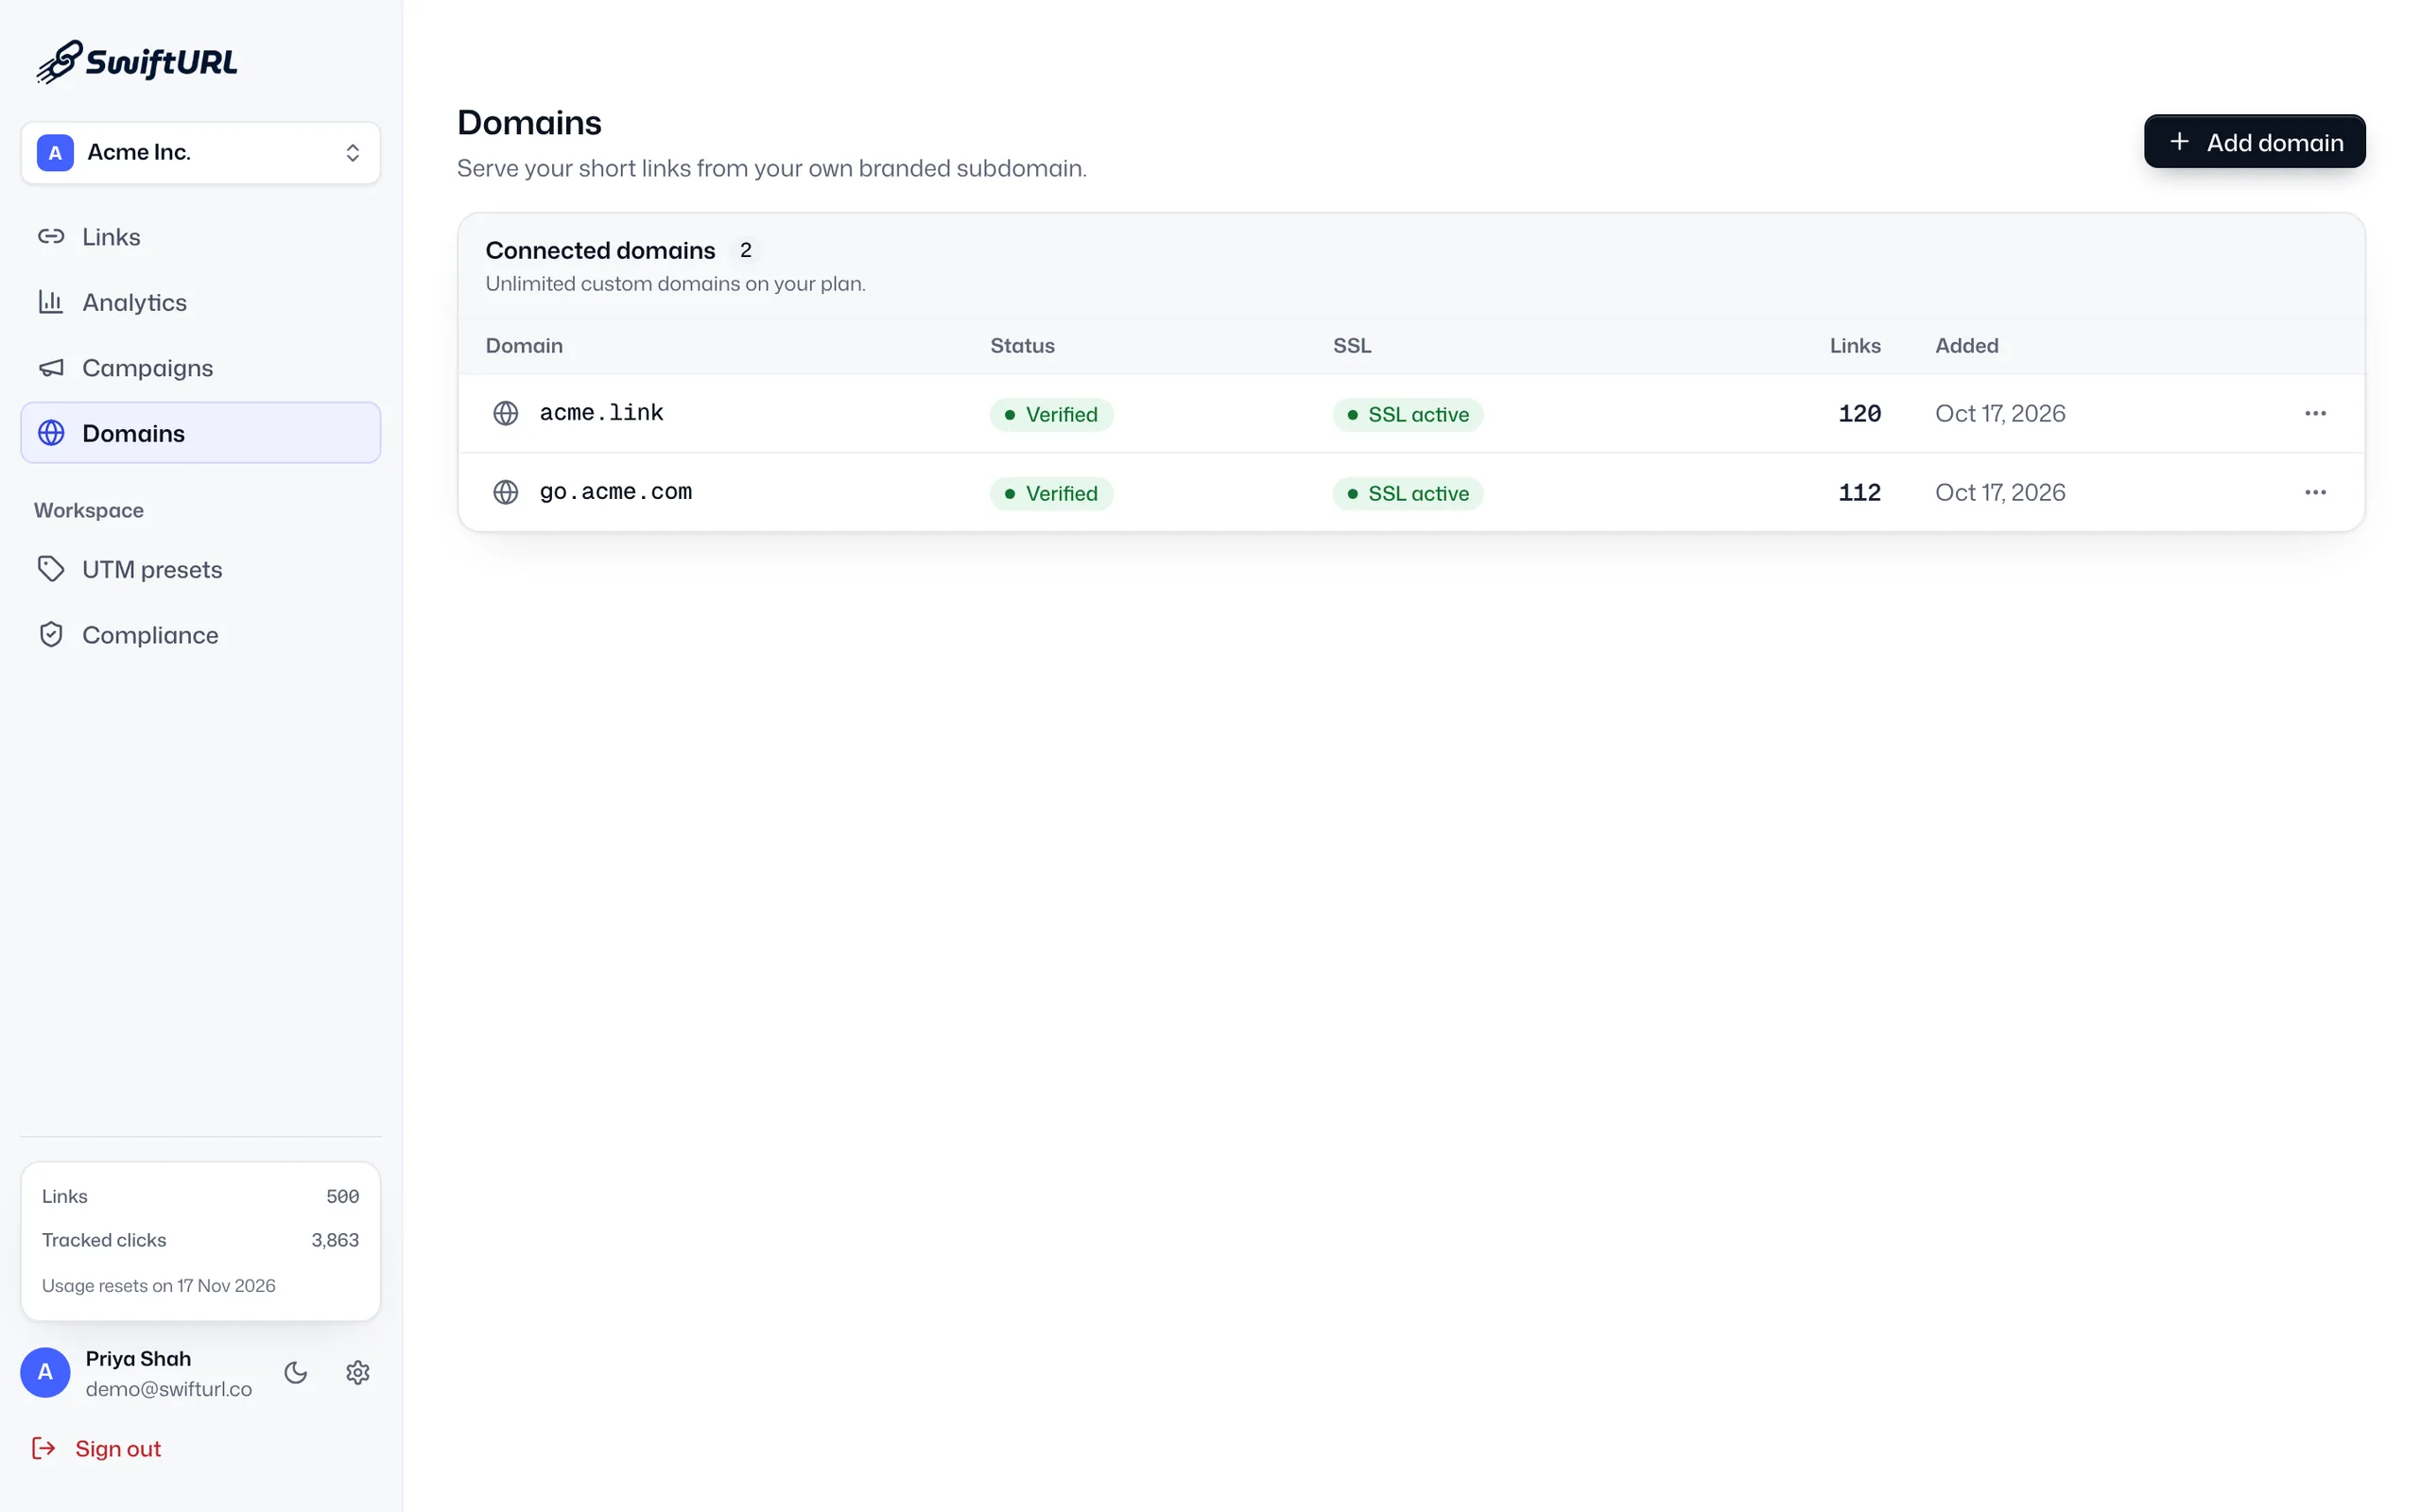
Learn moreServe short links from a domain you control, with SSL provisioned automatically.
Learn moreTurn on Deep View and deferred deep linking per domain, and wire the token in with a few lines in your app.